SecLayer
Enterprise Firewall Security Made Simple

An nftables/iptables based firewall, login failure daemon, and intrusion detection system for Linux servers, now with a live connection map that shows who is on your server in real time.

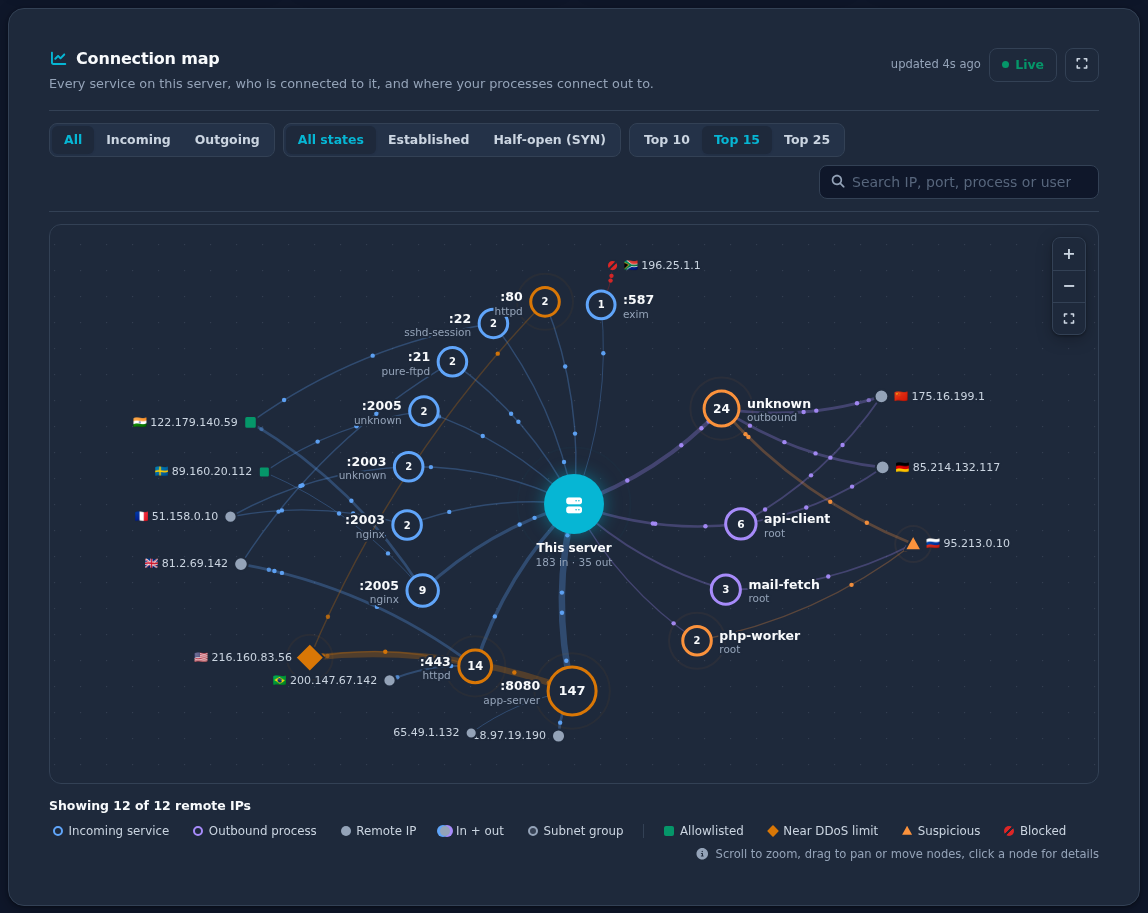
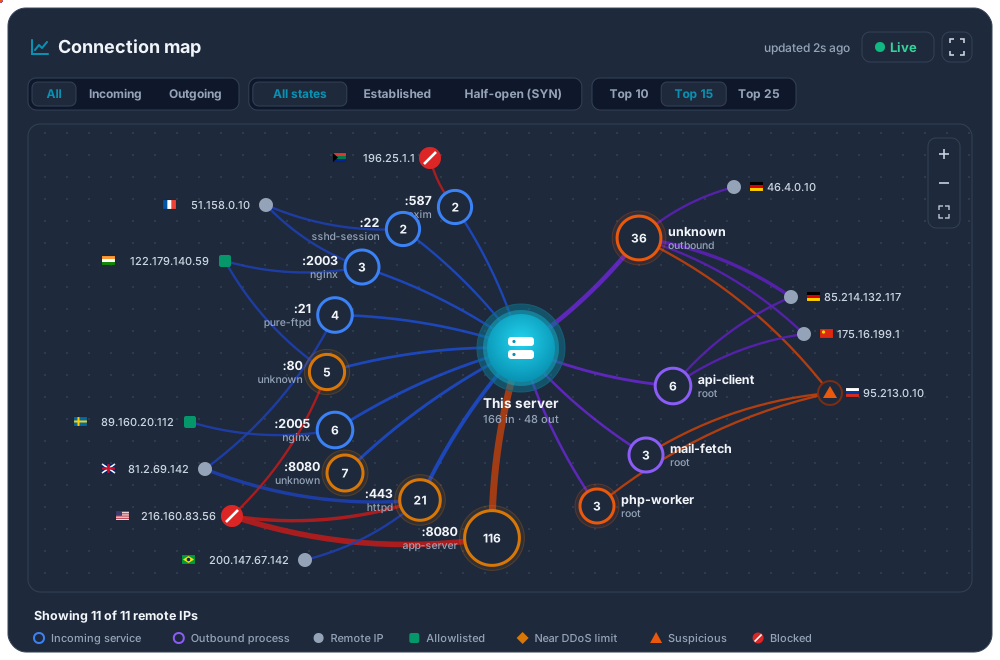
SecLayer live connection map: services, processes and remote IPs with live traffic

See Every Connection As It Happens

A live, animated map of your server: who is connecting to your services, where your processes connect out to, and which IPs need attention right now. Block attackers in one click.

  • Real-time network mapServices, outbound processes and remote IPs with country flags, updated every few seconds. Moving packets show which way traffic is flowing.
  • Spots trouble for youIPs near the DDoS limit, SYN floods, blocked IPs that are still connected, and processes talking to mining, spam or IRC ports are flagged automatically.
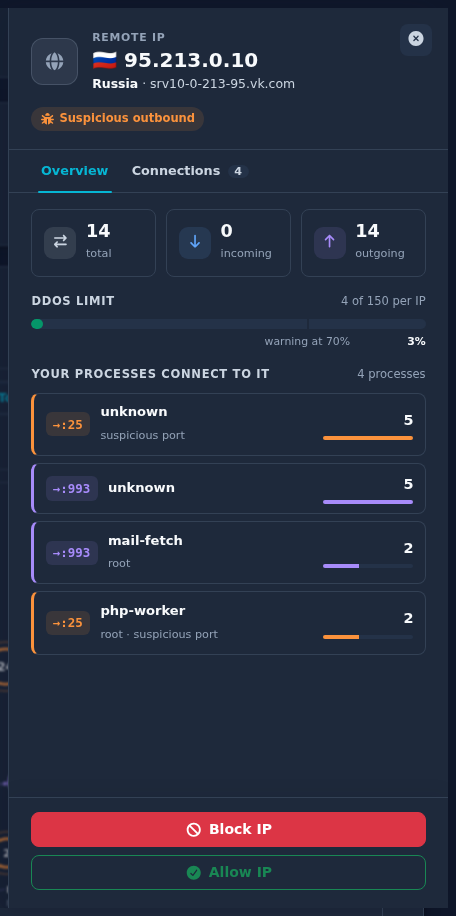
  • One-click responseOpen any IP to see its country, reverse DNS, DDoS limit gauge and every flow, then block or allow it. Block a whole subnet or many IPs at once.
  • Scales to thousands of connectionsTop 10 / 15 / 25 busiest IPs get their own node and the rest fold into subnet groups. Filter by direction, state, IP, port, process or user.
  • On your dashboardA compact live map sits on the SecLayer dashboard, so you see who is on your server the moment you log in.
Read the guide →
SecLayer connection map showing services, processes and remote IPs
IP details drawer with DDoS limit gauge and Block / Allow buttons

Install. Monitor. Protect.

SecLayer turns a complex security stack into a single, self-configuring system. No tuning, no maintenance, no blind spots.

One Command. Zero Configuration.

Run a single install command on any major Linux distribution. The installer automatically detects your OS, control panel, and running services - then configures everything with security best practices applied by default.

  • Auto-detects CentOS, RHEL, AlmaLinux, Rocky, Ubuntu, Debian, CloudLinux
  • Integrates automatically with Webuzo and cPanel/WHM, with more panels on the way
  • Lightweight Perl core with no PHP or database dependencies
  • Detects existing CSF installations and migrates your lists and settings in one command; CSF is disabled, never uninstalled
Installation Output
wget -O seclayer.sh https://a.softaculous.com/seclayer/files/install.sh chmod 0755 seclayer.sh ./seclayer.sh [OK] Detected OS: AlmaLinux 9 x86_64 [OK] Detected control panel: Webuzo [OK] Firewall rules applied [OK] LFD daemon started

Real-Time Visibility Across All Services

The Login Failure Daemon continuously tails authentication logs across every service on your server - from SSH and FTP to email and control panel logins. Nothing escapes detection.

  • Monitors 20+ log file types simultaneously with zero overhead
  • Tracks SSH, FTP, SMTP, POP3, IMAP, cPanel, Webmail, and more
  • Configurable failure thresholds per service type
  • PTR record lookup with regex pattern matching against offending IPs
LFD Activity Log
2026-05-30 10:37:50 server lfd[2050]: Daemon started - SecLayer lfd v1.0.0 2026-05-29 14:32:01 server lfd[2050]: LF_SSHD: 203.0.113.42 - 12 failures in 60s 2026-05-29 14:32:01 server lfd[2050]: BLOCKED: 203.0.113.42 added to nftables/iptables 2026-05-29 14:31:45 server lfd[2050]: LF_FTPD: 198.51.100.17 - 8 failures in 120s 2026-05-29 14:31:30 server lfd[2050]: LF_SMTP: 192.0.2.88 - 15 failures in 300s 2026-05-29 14:31:30 server lfd[2050]: BLOCKED: 192.0.2.88 added to nftables/iptables

Automatic Firewall Enforcement

When an IP exceeds your configured thresholds, it's immediately blocked at the nftables/iptables level with zero manual intervention. Blocks automatically expire after a configurable duration - no cleanup needed.

  • Instant nftables/iptables blocking with per-IP tracking
  • Configurable temporary and permanent block lists
  • Auto-expiry with permanent blocking for repeat offenders
  • Full IPv4 and IPv6 support with stateful connection tracking
Firewall Status
root@server:~# seclayer -l Chain INPUT (policy DROP) num target prot opt source destination 1 ACCEPT tcp -- 0.0.0.0/0 0.0.0.0/0 tcp dpt:22 2 ACCEPT tcp -- 0.0.0.0/0 0.0.0.0/0 tcp dpt:80 3 ACCEPT tcp -- 0.0.0.0/0 0.0.0.0/0 tcp dpt:443 4 DROP all -- 203.0.113.42 0.0.0.0/0 5 DROP all -- 198.51.100.17 0.0.0.0/0 6 ACCEPT all -- 10.0.0.0/8 0.0.0.0/0

Stay Informed, Not Overwhelmed

Configurable alerts keep you in the loop without notification fatigue. Per-event type settings, smart aggregation, and frequency throttling ensure you never miss a critical event.

  • Per-event-type email alerts with custom templates
Alert Configuration
# /etc/seclayer/seclayer.conf TESTING = "0" LF_ALERT_TO = "[email protected]" LF_ALERT_FROM = "[email protected]" LF_ALERT_SMTP = "mail.example.com" PTR_ALLOW = "1" IGNORE_ALLOW = "0"

Complete Protection Out of the Box

Integrated security modules and tools that work together to provide comprehensive server protection. No assembly required.

New

Live Connection Map

See every service, outbound process and remote IP on your server in real time. Flags IPs near the DDoS limit, SYN floods and suspicious outbound ports, and blocks them in one click.

Learn more →

Login Failure Daemon

Automatically blocks brute force attacks across 20+ services. Prevents credential compromise with real-time log monitoring and instant nftables/iptables enforcement.

Learn more →

Dynamic Firewall

Self-configuring nftables/iptables firewall that scans your services and builds precise allow/deny rules automatically. IPv4, IPv6, and custom port support.

Learn more →

DDoS Mitigation

Connection-based DoS protection at L3/L4 with per-IP connection limits, port flood detection, and ICMP rate limiting.

Learn more →

Intrusion Detection

Port scan detection, exploit pattern matching, and suspicious process tracking. Regex-based log analysis identifies known attack signatures in real time.

Learn more →

Alerting & Notifications

Configurable alerts via email with smart throttling and aggregation that prevent notification fatigue while keeping you informed.

Learn more →

Account Hardening

Alerts on new account creation, monitors file integrity, and detects deleted-binary processes across all accounts - from root to reseller to end-user.

Learn more →

Country & ASN Blocking

Deny or allow whole countries or networks (AS numbers) with CC_DENY and CC_ALLOW. Zone data refreshes automatically, so new ranges are covered without any work.

Learn more →

Security Check

A guided checklist of the essentials: allow your own IP, keep SSH and panel ports open, start the firewall and set alerts, each with a one-click fix.

Learn more →

Works With Your Control Panel

Seamless integration with every major hosting platform. Panel-specific features activate automatically when detected during installation.

cPanel / WHM

Fully Supported

DirectAdmin

Coming Soon

Plesk

Coming Soon

InterWorx

Coming Soon

CWP

Coming Soon

SecLayer vs. CSF

SecLayer is a modern, actively maintained alternative to ConfigServer Security & Firewall (CSF), familiar to CSF users and built for today's threats.

Feature SecLayer CSF
Live Connection Map ✓ Real-time map with one-click blocking ✗ Not included
Login Failure Daemon (LFD) ✓ 20+ services ✓ 20+ services
Dynamic Firewall ✓ Auto port discovery ✓ Manual configuration
Intrusion Detection ✓ Port scan & log monitoring ✓ Port scan & log monitoring
Account Hardening ✓ File integrity & process tracking ✓ File integrity & process tracking
Guided Security Check ✓ Checklist with one-click fixes ✗ Not included
DDoS Deflate ✓ Included ✗ Not included
Webuzo Plugin ✓ One-click install ✗ Manual setup
Software Updates ✓ Active ✗ Stalled (Discontinued)
Development Status ✓ Active ✗ End of Life (EOL)

Common Questions Answered

Which Linux distributions are supported?
SecLayer supports CentOS, RHEL, AlmaLinux, Rocky Linux, Ubuntu, Debian, and CloudLinux on 64-bit architecture. The installer automatically detects your distribution and configures all components accordingly - no manual setup required.
Do I need a control panel to use SecLayer?
Not at all. SecLayer works perfectly on standalone Linux servers. When a supported control panel is detected, additional integration features such as user tracking and service monitoring become available automatically - but they're never required.
How is SecLayer licensed?
SecLayer costs $5 per server per month, and it is free on any server with an active Softaculous license. See Pricing for details.
How much does deployment impact server performance?
Minimal. SecLayer is written in Perl with no PHP or database dependencies, and the login failure daemon uses negligible CPU during normal operation.
How does SecLayer handle false positives?
Thresholds are configurable per service type, and you can maintain permanent allow lists for trusted IPs. The ignore list feature excludes specific IPs from LFD tracking. Temporary blocks expire automatically, and administrators can manually unblock IPs through CLI or dashboard.
Can I customize how alerts are sent?
Yes. Alerts are configurable on a per-event-type basis with custom message templates. You can receive alerts via email or custom integration scripts that hook into your existing monitoring stack.

Ready to Secure Your Infrastructure?

Deploy SecLayer on your servers in minutes. Free on servers with a Softaculous license, $5/server/month otherwise.